LiteLLM Suffers Supply Chain Attack, Malicious Version 1.107.0 Steals Sensitive Data

 Prefer us on Google


LiteLLM has once again fallen victim to a supply chain attack, with the malicious version litellm@1.107.0 affecting PyPI packages and Docker images, including tags such as latest and main-stable. The injected malware executes automatically upon Python startup, stealing sensitive data such as cloud credentials, AI API keys, and SSH private keys, and supports remote code execution. Users are advised to avoid using version 1.107.0, and it is recommended to rebuild the environment from a clean image and rotate any potentially compromised credentials, while sticking to version 1.106.2.
-- Price
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
Swell DAO Admin Keys Suspected of Being Compromised, Malicious Contracts Threaten to Steal 2,500 ETH
Railway Security Incident: Potential Leak of User Environment Variables and API Keys, All Deployments Suspended
Anthropic Launches Research Preview of Claude Duet
NEAR AI tops 1 million tokens staked as rewards fund AI inference
Anthropic PBC Plans Spending Up to $750 Billion Before IPO
CoreWeave Launches Physical AI Launchables to Simplify Physical AI Workloads
Jensen Huang: Future Telecom Base Stations Expected to Evolve into Distributed AI Networks, All Telecom Operators Will Provide AI Computing Power
FSB Proposes 12 Practices for AI Governance in Financial Institutions
Aethir Updates ATH Token Economic Mechanism, Daily Burn Mechanism Launches in November
Morgan Stanley: What Can the U.S. Midterm Elections Change? AI and Fiscal Policy Take Center Stage
Is 2008 Repeating? CDS Returns to Market Focus
Anthropic Reports $16.3 Billion Revenue in First Half, Future Computing Commitments May Reach $75 Billion
Grayscale Research Director Says Decline in Computing Stocks, Demand Will Remain
Google Cloud Outage: Revolut Paralyzed, Crypto Balances Show Zero
MoneyGram Joins XDC Network as Institutional Validator
Morgan Stanley Warns of Multiple Risks in U.S. AI Infrastructure Investment, Predicts 32 GW Power Shortage by 2028
Xie Jiayin: TiDB Cloud Hacked, Bitget Suspended for Two Months Without Data Leakage
Capital as Production Capacity: Where Did the Money of the Top 100 VC and CVC in the U.S. Go in the First Three Quarters of 2026?
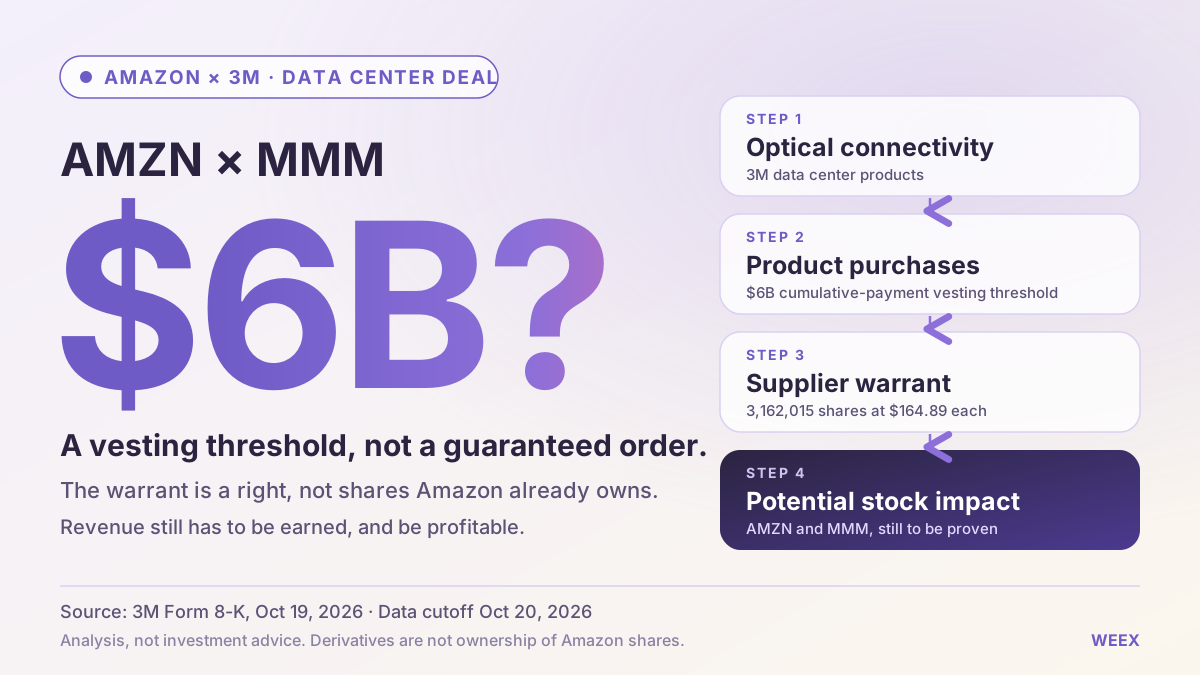
Amazon’s 3M Data Center Deal: What It Means for Amazon (AMZN) and 3M (MMM) Stock
Assess Amazon’s 3M data center deal, the $6 billion warrant threshold, potential dilution, and what the agreement could mean for AMZN and MMM stock.
Why Are Companies Reducing AI Spending? What It Means for AI Stocks
Elice Group IPO Plummets 28% on First Day
Bitdeer AI Cloud Business Backlog Reaches $2.9 Billion, Bitcoin Production Grows 200% in September
Phala Cloud Attacked, Some Customer Logs and Environment Variables Read
CITIC Securities: Market Overestimation of CoreWeave Concerns, New Cloud Providers' Short-Term Funding Gap 'Still Manageable'
Global Economic Resilience Faces Test as High Rates and Supply Risks Impact Asset Allocation
10-Year Yield Plummets 17 Basis Points in a Week! AI Trading Turmoil Rekindles Safe-Haven Attributes of U.S. Treasuries
Ministry of Commerce Promotes Application of New Technologies such as Blockchain to Enhance Trade Development
Goldman Sachs Throws Out 'Chilling Chart': Either the Bond Market is 'Overly Pessimistic' or the Stock Market is 'Too Optimistic'
Jieyue Xingchen Launches STEPX Neo Phone with AI Integrated into the Operating System
E Wei Nan: AI Drives Equality in Scientific Research, Future Citizen Scientists Will Become Main Force
Swell DAO Admin Keys Suspected of Being Compromised, Malicious Contracts Threaten to Steal 2,500 ETH
Railway Security Incident: Potential Leak of User Environment Variables and API Keys, All Deployments Suspended
Anthropic Launches Research Preview of Claude Duet
NEAR AI tops 1 million tokens staked as rewards fund AI inference
Anthropic PBC Plans Spending Up to $750 Billion Before IPO
CoreWeave Launches Physical AI Launchables to Simplify Physical AI Workloads




